Every technology that powers a business also introduces a layer of security responsibility. Programming languages, web servers, open-source libraries, code repositories, and cloud infrastructure all depend on components that must remain secure and up to date.
Actually, a single overlooked vulnerability can create a chain of exposure, putting applications, sensitive information, and business operations at risk.
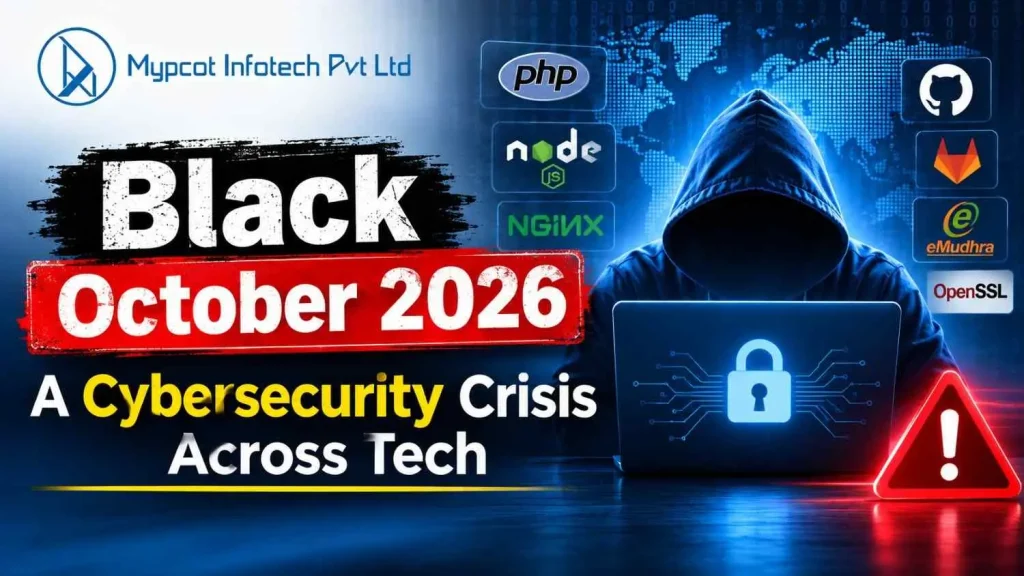
October 2026 has brought this challenge into sharper focus, with security concerns emerging across widely used technologies. Black October 2026 highlights the growing impact of critical cybersecurity vulnerabilities and why businesses need to go beyond individual software updates in order to protect their entire technology stack.
Table of Contents
ToggleA Wave of Critical Cybersecurity Vulnerabilities Across Major Technologies
A vulnerability in one software component can expose numerous connected systems. A flaw in a programming runtime can affect the application server, while a weakness in a code repository could put source code and deployment credentials at risk. And October 2026 has brought these interconnected security concerns into focus across several widely used technologies. Here are the major areas businesses and developers should pay attention to:
PHP: Critical PHP2Shell Vulnerabilities
PHP security concerns have gained attention following reports of two PHP2Shell flaws, CVE-2026-109618 and CVE-2026-109619, associated with remote code execution (RCE).
Exploitation could allow attackers to execute commands on vulnerable servers, potentially compromising application and stored data. Businesses should:
- Discover affected PHP versions and apply the relevant security patches.
- Restart PHP services where required.
- Check server logs for suspicious activity.
- Remember that updating WordPress plugins does not patch the underlying PHP runtime.
Node.js: Runtime and Dependency Security Risks
Node.js applications depend heavily on npm packages, and this makes dependency security an important part of vulnerability management. A flaw in a third-party package can also affect authentication request handling, file processing, or sometimes application data.
Developers should review Node.js security advisories, audit direct and indirect dependencies, and update vulnerable packages. Reviewing lockfiles and software bills of materials (SBOMs) can help identify hidden dependencies.
NGINX and Apache: Web Server Vulnerabilities
NGINX and Apache manage incoming traffic and connect users to applications. Vulnerabilities in request processing, server modules, or even access controls can affect applications that depend on a properly maintained web server.
Administrators should update affected versions, disable unnecessary modules, restrict exposed services, and review server configurations. A secure application still depends on a properly maintained web server.
GitHub and GitLab: Risks to Source Code and CI/CD Pipelines
Development platforms contain more than source code. They mostly store access tokens, deployment credentials, repository permissions, and automated workflows as well. A weakness in these environments can create a route into production infrastructure.
Key security measures include:
- Auditing repository and user permissions.
- Rotating potentially exposed access tokens.
- Updating self-hosted GitLab installations.
- Restricting CI/CD pipeline permissions and securing deployment credentials.
eMudhra: Digital Trust and Certificate Security
Digital trust platforms support electronic signatures, identity verification, and certificate-based authentication. A confirmed security flaw in these services could affect authentication processes or the integrity of digital transactions.
Organisations using eMudhra should monitor official security advisories and review affected certificates, credentials, or integrations if remediation is required. The specific product and impact must be verified before reporting an October 2026 incident.
OpenSSL: Vulnerabilities in Cryptographic Infrastructure
OpenSSL supports encrypted communication across websites, APIs, and applications. A vulnerability in this library can affect multiple services that depend on it for TLS connections and certificate handling.
Security teams should identify deployed versions, review official advisories, and update affected installations. They should also check applications that bundle their own OpenSSL libraries.
Why These Vulnerabilities Pose Serious Risks to Businesses
The real danger of critical cybersecurity vulnerabilities lies in how far their impact can spread. An exploited server flaw may give attackers access to application files, while compromised development credentials can expose repositories and deployment environments.
The real danger of critical cybersecurity vulnerabilities:
- Remote code execution: Attackers may run unauthorised commands on vulnerable servers, potentially install malicious software, access internal systems, or gain control over application environments.
- Sensitive data exposure: Customer records, employee details, financial information, API keys, and business credentials may become accessible, creating privacy and compliance risks.
- Software supply-chain compromise: A vulnerable dependency or development tool can affect multiple applications, making one security weakness a potential entry point across several systems.
- Operational disruption: Compromised servers, databases, or deployment pipelines can interrupt services, delay releases, and affect business continuity.
- Financial and reputational damage: Investigation, recovery, regulatory obligations, and customer notification can increase incident costs, while lost trust may affect long-term business relationships.
How Businesses and Developers Can Respond to Critical Vulnerabilities
It requires a systematic approach to manage critical cybersecurity vulnerabilities. Businesses should not only fix known security flaws but also identify how exactly they entered the environment and prevent similar risks from affecting other systems.
1. Identify affected software:
Start by checking the versions of operating systems, programming runtimes, servers, plugins, and third-party dependencies used across your infrastructure.
2. Prioritise and apply security patches:
Start by checking versions of operating systems and programming runtimes, servers, plugins, along with third-party dependencies used across your infrastructure.
3. Review access permissions:
Allow multi-factor authentication, remove unused accounts, rotate exposed credentials, and ensure users have access only to the resources they need.
4. Secure development environments:
Audit GitHub and GitLab repositories, CI/CD pipelines, build servers, API and GitLab repositories. CI/CD pipelines, build servers, API Keys, and deployment credentials. Keep development and production environments properly separated.
5. Monitor system activity:
Review server logs, authentication attempts, network traffic, and unexpected changes to application files. Investigate unusual activity that could indicate an attempted or successful attack.
6. Prepare for recovery:
Maintain regular, isolated backups and test whether they can be restored. Establish an incident response plan so teams know how to contain threats, investigate compromised systems, and restore services.
Effective vulnerability management does not end with patch installation. Businesses must verify that fixes work, investigate possible prior exploitation, and continuously monitor their technology stack to reduce future exposure.
Conclusion
October 2026 highlights how quickly unaddressed security flaws can put whole technology environments at risk. Everything, from application servers to development platforms, critical cybersecurity vulnerabilities require timely action, continuous monitoring, along with a proactive security strategy.
Businesses must make vulnerability management an ongoing priority instead of a one-time task. Mypcot Infotech helps businesses build and maintain more secure digital solutions, reducing technology risks and strengthening their overall security practices.